Hardware Root Of Trust Pufsecurity Puf-based Safety Ip Solutions Safe The Related World
One of essentially the most fundamental uses of a RoT is to maintain private crypto keys (encrypted data) confidential, protected by hardware mechanisms and away from the system software program that’s simpler to hack. The RoT’s safe storage and crypto functions should have the ability to deal with the keys and trusted processing needed for authentication of the gadget, verifying claims and encrypting or decrypting information. This can forestall malicious AI workloads and agents from operating and stop information from compromise or manipulation. However, a root of belief does not assess mannequin conduct or decide mannequin security. A Root of Belief is broadly defined because the safety basis for a semiconductor or digital system. Any safe function performed by the system or system depends in complete or in part on that Root of Trust.
Oci Hardware Root Of Belief
A Root of Trust is a set of core functions, generally applied in devoted, protected hardware (e.g., a particular chip or module), that’s assumed to be all the time trustworthy. Since this element cannot be modified, it provides the primary level of cryptographic verification in a system, making certain that all subsequent loading components (firmware, bootloader, kernel) are respectable and untampered with. Root of Belief is the foundation of security on which your computing system and linked cellular devices depend on. Cryptographic safety requires keys to encrypt and decrypt information, in addition to carry out different functions like producing and verifying digital signatures. Because Root of Trust schemes are inherently trusted, they have to be secure by design.
See how security is fundamental to the architecture of Oracle Cloud Infrastructure with tiered defenses and highly secure operations. Root of Belief is a building block for securing Web of Things (IoT) safety. Connecting IoT devices to your network creates limitless choices for integration but also can create loopholes that might be exploited by hackers and other dangerous actors. While a hardware Root of Belief offers significant safety benefits, it also introduces particular considerations for system designers. The RoT is crucial for contemporary security and privacy across various sectors, from consumer electronics to enterprise servers. In contrast, a wise door lock for a house or lodge would possibly need a PSA Licensed Degree three chip to guard in opposition to somebody using side-channel assaults within the night time to open the door.
Key Phrases Appendix
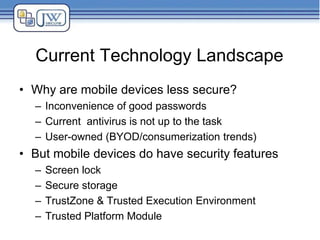
Root of Belief schemes generally embrace hardware hardening applied sciences like a hardware security module (HSM). HSMs are hardened, tamper-resistant hardware gadgets that safe cryptographic processes by generating, defending, and managing keys used for encrypting and decrypting knowledge and creating digital signatures and certificates. HSMs are examined, validated, and licensed to the highest security standards together with FIPS and Widespread Criteria. Entrust is a leading global provider of HSMs with the nShield General Purpose HSM product family.
Safe Boot is the first application of RoT, guaranteeing that the operating system has not been compromised by rootkits or malicious bootloaders. By verifying each stage of the boot process, Safe Boot ensures that a device runs only software trusted by the Authentic Gear Producer (OEM). This prevents attackers from replacing the OS with a modified version designed to steal data or listen in on communications. Root of Belief (RoT) is a source that may always be trusted within a cryptographic system. As A Result Of https://www.hocbench.com/things-to-consider-when-choosing-computer-recycling-louisville-ky/ cryptographic security depends on keys to encrypt and decrypt knowledge and carry out capabilities similar to producing digital signatures and verifying signatures, RoT schemes usually embrace a hardened hardware module. A principal instance is the hardware security module (HSM) which generates and protects keys and performs cryptographic capabilities inside its secure surroundings.
Selecting An Adequately Secure Rot
- It provides an easy-to-use security part applied by many of the world’s leading chip distributors.
- These accelerators allow the device to perform advanced mathematical operations with out burdening the primary CPU.
- Scale Back the risk of firmware-level attacks towards cloud tenants with root of belief expertise designed to wipe and reinstall the firmware each time a brand new server is provisioned or a new customer tenancy is established.
- They additionally be certain that cryptographic operations happen within a trusted setting, stopping delicate data from being uncovered in system reminiscence.
- Increasingly additionally it is coated by regulation, regulation and requirements so security can’t be added as an afterthought.
This key’s the basis for all safe operations, corresponding to native on-device asset safety for identification, authentication, and safe communication with the exterior setting. As such, the RoT should at all times be trusted by the system and is finest carried out as a Hardware Root of Belief (HRoT) for optimum protection. Root of Trust is becoming more and more essential as the use of Web of Things (IoT) devices becomes increasingly common. To thwart hacking attempts, elements of computing methods and related cell devices want a way to confirm if the data they are receiving is authentic. The IoT Root of Trust helps build trust in the whole computing ecosystem by safeguarding the security of knowledge and applications inside it.
While it’s attainable to implement a root of belief in software program, it is typically thought of insufficient for high-security environments. This is as a result of a software-based RoT resides in the identical memory area as the potential threats it’s designed to detect, making it susceptible to the identical exploits that compromise the operating system. If the underlying operating system is compromised, the muse of belief is damaged. The Chain of Belief is a hierarchical course of where each part verifies the integrity of the subsequent component earlier than handing over management. This chain creates a safe hyperlink from the hardware all the way as much as the applying layer. If any link within the chain fails verification, the method halts or flags an error, stopping compromised code from working.
Every secure system needs an anchor — a component that’s trusted unconditionally as a end result of every little thing else’s trustworthiness depends on it. It’s the first thing that executes when energy is applied, and its integrity determines whether something that follows may be believed. For secrets administration, hardware-backed controls scale back the risk of exposing delicate keys, tokens, and credentials. Platforms corresponding to Hexnode can support organizations by serving to enforce system security posture, configuration policies, and compliance necessities around trusted endpoints. Working the gamut from small, restricted security implementations to larger, excessive safety anchors, the choice of a root of trust is finest tied to the distinctive technical and enterprise wants of the chipmaker and its customers.
Reduce Risk From Assaults Or Backdoors In Firmware
Roots of belief aren’t one-size-fits all, so before adopting one you will need to evaluate your safety needs.