Hardware: Open-source Silicon Root Of Trust Rot Formtek Blog
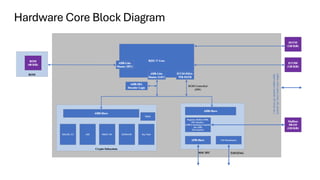
Moreover, the OpenTitan default configuration is provided with 2MB of flash reminiscence, which might be difficult to fit inside the obtainable silicon space, a specification of the reference SoC.We present an extension to the flash controller datapath, described in Determine 7, which doesn’t require the presence of an embedded flash IP and permits loading code from an external SPI flash.We also reduced the data partition’s bank dimension from 2MB to 64KB to suit inside the silicon area imposed by the specifications. ARM TrustZone (Ngabonziza et al., 2016; Pinto and Santos, 2019) is a security extension for ARM processors, it offers features similar to secure boot and cryptographic operations, enabling the creation of safe and non-secure execution environments on a single chip. It is commonly used in, however restricted to, ARM-based cell units and embedded methods to establish a safe basis. After these steps, the Flash image can both verify and boot on the OpenTitan platform’s totally different boot stages, such as boot loaders, or directly verify the host area firmware and boot the application processor. We extended the OpenTitan boot circulate to the applying processor, exploiting the mailbox and its interrupt, as proven in Figure eight. Having entry to the SoC reminiscence map, OpenTitan can configure the PLIC of the applying processor, enabling the mailbox to interrupt and carry out additional configurations.
The Chain of Belief is a sequential verification course of during which every system part is authenticated by a beforehand trusted component earlier than it runs. This creates an unbroken path of verified integrity from hardware power-on to operating system load and beyond. In late 2019, Google launched OpenTitan, an open-source project that gives the blueprint for a silicon root of belief, a plan designed to keep away from vendor lock-in. Run-time BMC protection is a safety function that continuously monitors threats and supplies notification companies.
Safety Center
- As these platforms are often employed in safety-critical fields, they have to be secure and dependable, guaranteeing safety properties corresponding to sensitive information, code safety, and software execution integrity and offering means to run commonplace platform-level security features efficiently, corresponding to secure boot.
- The focus of our study is the central digital architecture of the Earl Grey OpenTitan implementation, the top_earlgrey module, thus we didn’t embrace in our design the Analog Sensor Top (AST), despite its important function in OpenTitan’s security framework.
- This certainty is determined by the root of belief (RoT), the starting point for system belief and verification.
- We outlined the various implementation targets, allowing us to fetch the OpenTitan repository as a Git dependency into the reference SoC for the integration.
This algorithm processes an input message to supply a hash worth of mounted dimension, employing a one-way design that stops https://www.volumepillshelper.com/new-approaches-to-home-and-business-security/ reverse engineering or finding different inputs leading to the same hash value. HMAC generates a safe digest using cryptographic hash features, making a message authentication code that is decided by a secret key shared between the sender and recipient. OpenTitan contains an HMAC accelerator programmed to calculate SHA-256 and HMAC message digests. The front-end of the accelerator includes a memory-mapped FIFO the place the software pushes the following 64-byte information block for processing. As Soon As the FIFO is crammed, the accelerator automatically reads it and initiates an 80-cycle process to replace its internal state earlier than processing the following knowledge block.
Embedded Elements
The boot ROM of the appliance processor is programmed to attend for the mailbox interrupt or a debug request via JTAG. OpenTitan populates its payload register with the boot tackle earlier than elevating the interrupt of the mailbox. As Quickly As the mailbox interrupt is obtained, the appliance processor reads the boot tackle from the mailbox and jumps to it. This boot circulate extends OpenTitan’s safe boot to the application domain, making certain that the firmware the host executes is authenticated on high of the authentication of the lower boot levels inside the OpenTitan Root-of-Trust. Despite these developments, sure basic safety challenges persist since data stays susceptible to unauthorized access in reminiscence, and encryption keys are saved in clear within general-purpose reminiscence.
You grant Formtek a worldwide, perpetual, irrevocable, royalty-free, fully-paid, and transferable (including rights to sublicense) right to train all copyright, publicity, and moral rights with respect to any information you submit, hyperlink to or otherwise upload to this blog site. Some of the individuals posting to this weblog web site, together with the moderators, work for Formtek. Postings by these individuals are the private opinions of those people, not of Formtek. Their posted content is supplied for informational functions solely and isn’t meant to be an endorsement or illustration by Formtek or another celebration. Postings to this blog website may be outdated, invalid or inaccurate by the point you learn them.
The Endpoint Security Gap: Why Software Alone Just Isn’t Enough
Moreover, the wrapper is in charge of setting the AST-related inputs to a specific configuration that permits the top_earlgrey module to bypass the interactions with the AST. Wang et al. (Wang et al., 2021) introduced an energy-efficient crypto-coprocessor that helps important cryptography algorithms like AES, ECC, and SHA. This design, integrated throughout the RISC-V Rocket chip core, acts as a crypto-extension activated by customized instructions via the Rocket Coprocessor Interface. Similarly, Tehrani et al. (Tehrani et al., 2020) have contributed by including support for lightweight cryptographic algorithms tailor-made for quick encryption on IoT units, while Marshall et al. (Marshall et al., 2021) have implemented the draft of the official RISC-V ISA extension for scalar cryptography. These approaches alleviate the burden of executing cryptographic duties in software program, thereby enhancing total system performance. In IoT units, optimization of cryptographic workloads is often achieved via the combination of accelerators throughout the system-on-chip (Wang et al., 2021; Tehrani et al., 2020; Marshall et al., 2021).
These regulations provide the framework for fostering a security-first mindset and adopting safety by design engineering ideas. “One factor that CryptoManager allows is that as the silicon travels from facility to facility—for instance, from fab to wafer chopping to die packaging to testing packaged die to fabrication to integration into a tool like a phone—is to guarantee that the semiconductor gadget itself has manufacturer-specific keys put in there that nobody else can get to or manufacturer-specific capabilities enabled or disabled,” he defined. In distinction, says Woo, a silicon-based hardware root of trust offers a range of robust safety choices. With the ever-increasing spread of the RISC-V Instruction Set Architecture (ISA), many research efforts aim to enhance security options on top of RISC-V-based processors as properly (Ehret et al., 2020; Kumar et al., 2020).
A hardware Root of Belief is the security foundation for a semiconductor or electronic system. Any secure operate the gadget or system performs relies absolutely or partially on that Root of Belief. With hardware immutability and trustworthiness, a Root of Belief offers the trusted foundation that the system and the applying can use to construct their protection and implement the required confidentiality, authenticity, integrity, and other safety properties and attributes. Like with any complicated system, no answer is ever utterly secure or bulletproof towards sophisticated cyber-attacks. Multi-layered security and protection in depth technique is a cybersecurity core pillar for the automotive trade to successfully defend the information and assets within the vehicle.
Intel SGX (Zheng et al., 2021) (Software Guard Extensions) is a know-how developed by Intel that allows the creation of secure enclaves within the CPU, via customized extensions to the instruction set of the processor’s core. SGX supplies a hardware-based resolution for secure execution of code and protection towards both bodily and software attacks, and is broadly adopted in cloud computing environments. A root of belief operates via a “chain of belief,” a hierarchical system in cybersecurity where belief is established and handed down from a trusted “root” to intermediate entities, making certain authenticity. A chain of trust consists of a sequential cryptographic verification course of the place every component in the boot sequence is authenticated by the preceding, already trusted part earlier than execution.